In July 2026, the DPP Registry became operational, while 18 February 2027 marks the first major mandatory DPP milestone for certain battery categories. Other sectors, including textiles, tyres and aluminium, are also scheduled for DPP-related requirements during 2027.
Instead of landing on a generic product page, customers can access information about the product’s materials, origin, repair options, sustainability characteristics, or end-of-life handling.
Now imagine the same product information being useful to a repairer, recycler, supplier, manufacturer, or regulator. That is the idea behind the Digital Product Passport (DPP). If you want to understand how DPP software works in practice, explore our guide on use cases and features of a Digital Product Passport Software.
In this guide, we’ll break down the 2027 EU Digital Product Passport deadlines, the product categories moving toward DPP requirements, and—most importantly—what brands need to build behind the passport to be ready.
A Digital Product Passport isn’t just a QR Code
A product can be perfectly manufactured, labelled, and ready to sell in Europe—and still leave a big question unanswered:
- Can you prove where its materials came from?
- Who supplied them?
- How it should be repaired or recycled, and keep that information accessible throughout its lifecycle?
Product information is often spread across ERP systems, PLM software, supplier spreadsheets, compliance documents, manufacturing databases, and emails. One team may have material data, another may manage certifications, while supplier information sits somewhere else entirely.
The QR code may be what a customer sees. But, behind it, businesses need a system that is capable of collecting product data, connecting suppliers, managing product identifiers, integrating existing business software, and making relevant data available throughout the product lifecycle.
Turn DPP Compliance Into a Competitive Advantage with Triple Minds
Preparing for EU Digital Product Passport requirements takes more than adding a QR code. At Triple Minds, we build custom DPP software with product data management, supplier portals, system integrations, and digital passport workflows to help businesses prepare for evolving requirements.
Explore Digital Product Passport Software
The 2027 DPP Deadlines Brands Need to Know
Before we look at the dates, one thing that you should know is that there is no single DPP deadline in 2027 that applies to every product. However, the EU is introducing DPP requirements by product category and its current indicative timeline includes the following milestones:
| Timeline | DPP Development |
| 20 July 2026 | EU DPP Registry becomes operational |
| 18 February 2027 | DPP becomes mandatory for certain battery categories |
| Q2 2027 | Planned DPP requirements for construction products and service providers |
| Q3 2027 | Planned additional DPP service-provider requirements |
| Q3–Q4 2027 | Planned sector-specific requirements for textiles, aluminium and tyres |
| 2028 | Planned sector-specific requirements for furniture |
| 2029 | Planned requirements for mattresses and certain recycled-content/ICT-related areas |
1. Regulatory Context: The ESPR, CPR, and Battery Regulation Framework
The Digital Product Passport (DPP) is not a stand-alone policy. It is the regulation and data delivery mechanism that enables the wider European Union’s Circular Economy Action Plan (CEAP) and European Green Deal.
While the previously operating Ecodesign Directive focused on energy efficiency of appliances, the ESPR expands this to be about making products more sustainable, durable, repairable, reuseable and transparent.
The regulatory framework relies on three legal pillars:
- Ecodesign for Sustainable Products Regulation (ESPR — Regulation EU 2024/1781): This enforcement has set out a framework of rules around product durability, reusability, upgradability, repairability, microplastic release, recycled content and carbon footprint metrics.
- EU Battery Regulation (Regulation EU 2023/1542): Serving as the trailblazer regulation for the DPP, the regulation explicitly mandates digital passports for high capacity industrial, light means of transport (LMT) and Electric Vehicle (EV) batteries.
- Revised Construction Products Regulation (CPR — Regulation EU 2024/3110): It sets out parallel DPP requirements for building materials, structural products and construction components.
Due to these strict regulations, the burden of proof from post-market regulatory audits has shifted to pre-market digital verification. That means if your product is not compliant and is not DPP registered within the central EU DPP registry, goods will be blocked at customs and barred from the EU single market.
2. Phased Rollout Timeline (2026–2030): Why 2027 is the Turning Point
The European Commission is executing a phased rollout through sector-specific Delegated Acts. These legal acts outline the exact data fields, standards, and access permissions required for each industry.
2026: The Infrastructure & Pilot Phase
- July 19, 2026 — EU Central Registry Operations: The European Commission launches the official EU Digital Product Passport Registry. This registry will manage the Unique Product Identifiers (UPIs) and validate passport authenticity across customs borders.
- July 19, 2026 — Ban on Destruction of Unsold Goods: If major enterprises destroy their unsold products like apparel, clothing accessories, footwear etc., they will suffer an immediate ban. The penalty doesn’t end here. They may also face mandatory disclosure rules.
- Priority Rulemaking Begins: Regulatory draft frameworks advance for primary material streams, including iron, steel, and initial textile guidelines.
2027: The Mandatory Deadline for Batteries & Priority Sector Rulemaking
- Feb 18, 2027 — Mandatory Battery Passports: This is the first hard, and legally enforced Digital Product Passport deadline. From 18 Feb, 2027 LMT batteries, industrial batteries > 2kWh and E-Vehicles batteries in EU market should have an active, and compliant battery passport.
- Textiles, Apparel & Footwear: Draft Delegated Acts for apparel and footwear finalize their adoption stages, and set out data schemas for fiber traceability, recycled content percentages and microplastic shed ratings
- Tyres, Aluminium & Structural Materials: Priority rulemaking sets out baseline durability and carbon footprint calculators for automotive components and raw industrial inputs.
Read More: A Complete Guide To Build A Battery Recycling Management Software
2028–2029: Expansion to Consumer Goods & Construction
- Furniture & Mattresses (2028–2029): The EU maybe require furniture and mattresses to have a DPP containing information such as: chemical toxicity, material used, disassembly documentation and bio-based material certifications.
- Electrical & Electronic Equipment (2029): For products such as washing machines, TVs, laptops, or other electronics, the requirements could focus on governing repairability scores, spare part availability timelines and recycled plastic content.
- Construction Products (2026–2029 CPR Rollout): It indicates the progressive rollout of passports across construction material like concrete, insulation and architectural glass.
However by 2030, it is most expected that the ESPR framework will encompass the majority of manufactured physical goods distributed across the 27 EU member states. Not just this, the revolution can also include imported products manufactured in the US, UK, Asia and Latin-America.
A Complete Product Category Based Map
| Product Category | Regulatory Route | Expected Adoption | Estimated DPP Compliance |
| Batteries (EV, LMT & industrial >2 kWh) | Separate regulation | Adopted | February 2027 |
| Iron & steel | ESPR intermediate product | 2026 | ~2027–2028 |
| Textiles & apparel | ESPR final product | Late 2027 | ~2028–2029 |
| Tyres | ESPR final product | 2027 | ~2028–2029 |
| Aluminium | ESPR intermediate product | 2027 | ~2028–2029 |
| Household dishwashers | ESPR energy-related product | Q3 2027 (planned) | ~2029 |
| Furniture | ESPR final product | 2028 | ~2029–2030 |
| EV chargers | ESPR energy-related product | 2028 | ~2029–2030 |
| Fridges & freezers | ESPR energy-related product | 2028 | ~2029–2030 |
| Electric motors | ESPR energy-related product | 2028 | ~2029–2030 |
| Mattresses | ESPR final product | 2029 | ~2030–2031 |
| Mobile phones & tablets | ESPR energy-related product | 2030 | ~2031–2032 |
What Information Should a Compliant Digital Product Passport Contain?
A compliant Digital Product Passport is not a static PDF upload or an unverified marketing page. It is an interoperable, structured data asset. Depending on the industry-specific Delegated Act, a passport must deliver structured data across four core operational pillars:
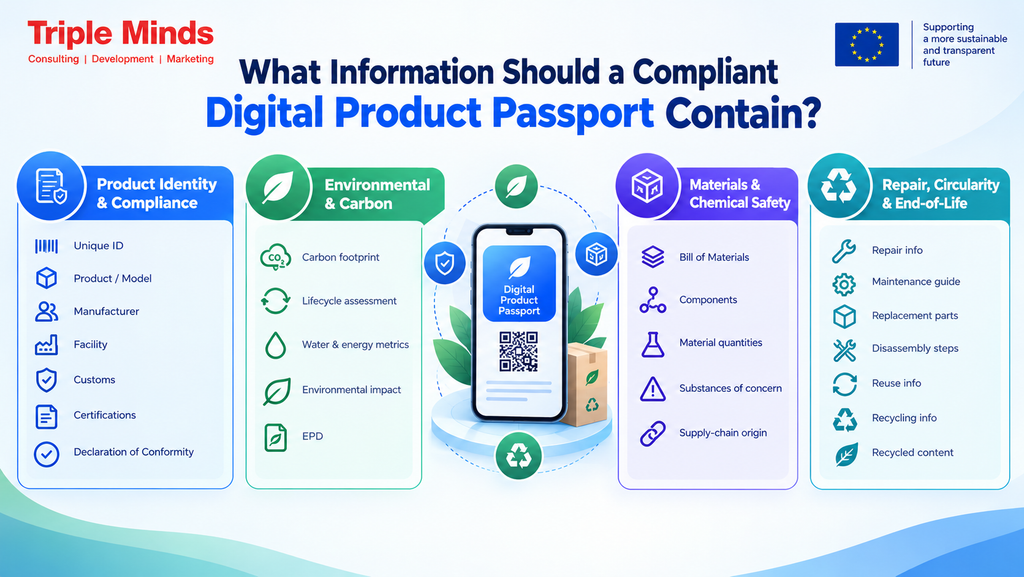
Product Identification and Compliance
First, the passport needs to identify the product. The core purpose behind product identification is to create a reliable connection between the physical product and its digital records. It can include:
- Unique product identifiers
- Product or model information
- Manufacturer details
- Facility information
- Relevant customs information
- Compliance documentation
- Safety certifications
- Declaration of Conformity information
Environmental and Carbon Information
For brands that have already invested in lower-carbon materials or more sustainable manufacturing, the DPP can provide a structured way to communicate and substantiate that information. DPP information can include environmental performance data. This may involve:
- Product carbon footprint information
- Lifecycle assessment indicators
- Water and energy-related metrics
- Environmental impact data
- Environmental Product Declarations
Read More: How Does Carbon Credit Issuance System Work?
Materials, Components and Chemical Safety
A DPP can also bring greater visibility into what a product is actually made of. This is particularly important for complex products where the manufacturer may depend on information from several tiers of suppliers. It can include the following:
- Bill of Materials (BOM)
- Raw materials
- Components
- Material quantities
- Substances of concern
- Relevant chemical information
- Supply-chain origin data
Repair, Circularity and End-of-Life Information
This is where a DPP can become more than a compliance record. DPPs can also support the later stages of a product’s lifecycle. Depending on the applicable requirements, this may include:
- Repair information
- Maintenance guidance
- Replacement-part information
- Disassembly instructions
- Reuse information
- Recycling information
- Recycled-content data
Technical Architecture: What Brands Need to Build for DPP Readiness?
Brands cannot just deploy a standard website landing page and call it a Digital Product Passport. The European Commission demands an open, decentralized technical architecture that will ensure long-term data accessibility without vendor lock-in.
Data Carriers & Open Standards
The first visible component is the data carrier. Every physical product must carry an ergonomic, machine-readable Data Carrier. Depending on the applicable requirements, it can involve a QR code, DataMatrix, NFC tag, or another machine-readable method.
But generating the code is only one part of the process – the data carrier needs to tie to the right product information and be usable throughout the product’s intended lifecycle.
Structured Product Data Layer
Brands need a reliable way to organise the information associated with their products.
That may mean creating a dedicated product-data layer that brings together information from segregated systems. It includes- ERP systems, PLM platforms, PIM systems, supplier portals, manufacturing systems etc.
Interoperability, APIs, and Decentralized Storage
- API-First System Integration: A brand’s DPP system should be able to dynamically aggregate data from the brand’s existing Enterprise Resource Planning (ERP), Product Lifecycle Management (PLM), Supply Chain Management (SCM), and Product Information Management (PIM) platforms.
- Decentralized Data Availability: The data about products should remain available even if the brand goes bankrupt or restructures. It can be achieved through decentralized object storage, web servers, or blockchain.
- ISO/IEC Compliance: The systems should comply with international data exchange standards such as ISO/IEC 15459 (unique identification) and the W3C Verifiable Credentials specifications.
Role-Based Access: Who Gets to See What?
A DPP may contain information for very different audiences. It is not necessary that a customer, repairer, and recycler should have the access to the same data. Therefore, role-based access makes the control an important part of the system design.
| User | Potential Information |
| Consumer | Product information, environmental characteristics, care and repair guidance |
| Regulator / Authority | Compliance documentation and relevant regulatory information |
| Repairer | Technical documentation, repair instructions and spare-part information |
| Recycler | Material composition, disassembly and handling information |
At Triple Minds, we can help manufacturers, importers, and distributors build their Digital Product Passport solution, compliant to their sector’s window.
What Happens When Product Information Changes?
A product passport isn’t necessarily a “create it once and forget it” record. Fluctuations like product changes, supplier changes, component changes, and certifications expiring impact DPP. Therefore, a DPP platform needs a way to manage updates without losing track of what changed. This is where features such as:
- Data versioning
- Approval workflows
- Audit trails
- Change history
- Validation rules
- Role-based editing
How Triple Minds Can Help with DPP Software Development
For Triple Minds, the opportunity isn’t simply to offer a “Digital Product Passport app.”
The bigger opportunity is helping brands build the technology infrastructure behind their DPP strategy. Depending on the business requirements, that can include:
Custom DPP Platforms
A central platform for managing product identities, product information, lifecycle data, users, and passport records.
Supplier Portals
A structured way for suppliers to submit, update, and validate material and component information.
ERP and PLM Integrations
Connecting existing business systems with the DPP environment to reduce duplicate data entry and keep information synchronized.
API Development
Creating secure APIs for exchanging information between internal systems, DPP platforms, service providers, and other relevant infrastructure.
Product Identity and QR Workflows
Connecting physical products with their corresponding digital records through appropriate data carriers.
Admin and Compliance Dashboards
Giving internal teams visibility into missing information, validation status, product records, and DPP readiness.
Role-Based Access
Creating different information views for customers, suppliers, repairers, recyclers, regulators, and internal teams.
Scalable Data Architecture
Designing a system that can handle growing product catalogues, product variants, batches, and lifecycle information.
The right solution will depend on the brand’s products, existing systems, suppliers, data requirements, and applicable regulations. The important thing is to start with the data and workflow, not the software screen.
Get Your Business Ready for EU Digital Product Passport Deadlines
Preparing for EU Digital Product Passport deadlines requires a clear compliance roadmap and the right expertise. Triple Minds offers consulting services to help businesses understand applicable requirements, assess product data readiness, identify compliance gaps, and plan the next steps toward DPP compliance.
Contact Our Experts Now
2027 Deadline is Here. Start Preparing with Your Data
The concept of a digital product passport may seem simple from the outside, but in reality it consists of a complex approach. From collecting and structuring product data to providing information, there are many functionalities. Existing business systems may need to communicate. Product identities need to stay connected to their digital records. Access needs to be controlled. And the information needs to remain accurate as the product moves through its lifecycle.
That’s why the 2027 EU DPP deadlines should be treated as a technology-planning milestone, not a last-minute compliance task.
For brands preparing for the upcoming EU requirements, Triple Minds can help transform DPP requirements into practical software. From custom DPP platforms and supplier portals to ERP/PLM integrations, APIs, product-data systems, and role-based digital experiences, we’ve got your back. Because when the deadline arrives, the question won’t be whether your product has a QR code. It will be whether the technology behind it is ready.
Digital Product Passport Software FAQs
No. A QR code or data carrier can provide a way to access the digital product information but, the underlying system needs to manage the relevant data, identifiers, access, updates and integration. Therefore, you can consider the QR as the doorway- actual DPP infrastructure is behind the doors.
No. An LCA may contribute environmental data to a DPP, but the passport can also contain product identifiers, compliance information, material details, repair guidance, and other product information.
Batteries are among the first major product categories facing DPP requirements in 2027. Other sectors, including textiles, tyres, aluminium and construction products, are also part of the broader DPP rollout. The exact requirements and timelines depend on the relevant product category and EU legislation.
Yes. Once product information is structured and connected, brands may be able to use DPP infrastructure to support repair services, resale, spare-parts management, recycling, take-back programs, customer engagement and better supply-chain visibility. This can turn a compliance requirement into a broader digital product-data capability.
Replika just paid €5 million. OpenAI paid €15 million seven months earlier. Both for the same thing — running an AI product on European users without the privacy paperwork. If you’re building an AI companion, that’s the bar now, and you cleared none of it on the day you registered the company.
GDPR compliance for AI companion startups is not the legal homework you do after you ship. It’s what decides whether your payment processor survives the first complaint, whether the Italian Garante puts you on its watchlist, and whether August 2026 — when the EU AI Act’s full enforcement layer lands on top of GDPR — ends your runway. This is the version we wish every founder we onboarded already had, in the plain language we use with our NSFW chatbot development clients on day one.
Building a Candy.ai-style or DreamGF-style app and want the privacy architecture baked in from commit one? Book a free consult at tripleminds.co/contact-us or see how we shipped Candy.ai.
The €5 Million Wake-Up Call: What Replika Got Wrong
On 19 May 2025, the Italian Garante fined Luka Inc. (Replika’s parent) €5 million. Not a slap on the wrist — a documented breakdown across seven GDPR articles:
| GDPR Article | What it requires | What Replika did wrong |
|---|---|---|
| Art. 5(1)(a) | Lawful, fair, transparent processing | Couldn’t point to a clear lawful basis |
| Art. 6 | Identify a lawful basis | None identified in writing for the data flows |
| Art. 12 + 13 | Clear privacy notice before collection | Notice was vague and scattered |
| Art. 5(1)(c) | Data minimisation | Collected more than the service needed |
| Art. 24 | Demonstrate compliance | Couldn’t |
| Art. 25(1) | Data protection by design | Architecture wasn’t designed with GDPR in mind |
The Garante then opened a second investigation into whether Replika’s training data was lawfully sourced. That’s the playbook now: fine you for the app, investigate you again for the model. Same dance with OpenAI in December 2024 — €15 million plus a mandatory six-month media awareness campaign. OpenAI called it “disproportionate” and noted the fine was nearly 20× their Italian revenue. Regulators aren’t pricing the fine to your revenue — they’re pricing it to discourage the next founder. If your honest answer to “what’s our Article 6 lawful basis for storing conversation logs?” is “uh, terms of service?” — you are Replika in 2024.
The 9 Articles You Actually Need to Memorise
You don’t need to read all 99 articles. You need these nine:
| # | Article | Plain meaning | Where it bites |
|---|---|---|---|
| 1 | Art. 5 | Six core principles — lawful, fair, transparent, minimised, accurate, secure | Cited in almost every fine |
| 2 | Art. 6 | Lawful basis for every processing activity | “We have ToS” isn’t one |
| 3 | Art. 7 | Consent must be freely given, specific, withdrawable | Pre-ticked boxes = no consent |
| 4 | Art. 8 | Children need parental consent | Hence age-verification fines |
| 5 | Art. 9 | Special category data banned unless exception | Explicit consent for sexual / health-related |
| 6 | Art. 13/14 | Privacy notice at collection | Must name training-data use |
| 7 | Art. 17 | Right to erasure | Includes the model, not just the DB |
| 8 | Art. 22 | No fully-automated decisions with significant effect | Heavy disclosure for personalisation |
| 9 | Art. 35 | DPIA mandatory for high-risk processing | AI companion = always mandatory |
Almost every enforcement action against an AI product since 2024 cites three or more of those rows.
The DPIA: The One Document That Decides Whether You Survive
Article 35 says: if processing is “likely to result in a high risk to the rights and freedoms of natural persons,” you must do a Data Protection Impact Assessment before processing starts. AI companions tick every high-risk criterion — large-scale special category data, systematic profiling, new tech, vulnerable users. The question isn’t whether. It’s when — and the right answer is before your first European user signs up.
A defensible DPIA runs 25-60 pages: every data flow described, a necessity test, a risk assessment with mitigations, and a DPO sign-off. Cost from a privacy lawyer plus a technical architect: €8,000–€25,000. From 2 August 2026 the EU AI Act’s remaining provisions kick in, and the max penalty for deploying an AI agent without a documented DPIA climbs from €20 million to roughly €55 million. The DPIA is the cheapest insurance you will ever buy.
Need a DPIA that will survive a Garante inspection — not a templated PDF from a privacy SaaS? Our AI chatbot development team produces DPIAs as a deliverable on every NSFW build. Talk to us.
Article 9: The Trap Most Founders Miss
Your user types: “I’ve been feeling really anxious since my divorce, can you cheer me up?” That one sentence contains mental-health data, marital status, and emotional state — all Article 9 territory. Article 9 prohibits processing special category data by default. The realistic exception for a consumer AI companion is explicit consent (Art. 9(2)(a)) — separate, specific, granular, recorded, withdrawable.
AI companions routinely process this on every active user:
- Sexual orientation and preferences (Art. 9 special category)
- Mental and emotional health signals — loneliness, anxiety, sometimes suicidal ideation
- Biometric voice prints for voice chat
- Selfies / custom avatar inputs (often biometric)
- Behavioural profiling at scale — every message feeds personalisation (Art. 22)
The platforms that get fined bundled all of this into a single ToS checkbox. Replika did exactly that. Character.ai’s Italian deployment did the same. A half-dozen smaller apps the Garante walked off the App Store in 2025 did the same.
The consent UX that actually works
| Step | What you collect | What consent you record |
|---|---|---|
| 1 — age gate | DOB, country | Age confirmation only |
| 2 — account | Email, password | Contract basis (Art. 6(1)(b)) |
| 3 — companion setup | Avatar, name, persona | Contract basis |
| 4 — adult content opt-in | None | Explicit consent: 18+ content (Art. 9 sexual orientation) |
| 5 — emotional companion opt-in | None | Explicit consent: emotional/health processing |
| 6 — training opt-in | None | Explicit consent: chats used for model improvement (default OFF) |
| 7 — voice features | Voice sample | Explicit consent: biometric processing |
Training opt-in as a separate, off-by-default toggle is the single most defensible thing you can ship. It’s the exact thing the Garante called OpenAI out for not doing.
Right to Be Forgotten — When Your Model Won’t Forget
Article 17 makes every AI CTO sweat. The law says: if a user asks, you delete their personal data. Easy when it’s a row in Postgres. Not easy when their conversations live in a vector DB, an embedding, a fine-tune corpus, three observability tools, and a CDN cache. You need a deletion pipeline that hits all of those — and you need to prove it hit all of them:
[Erasure Request] → [User-ID Resolver]
                         │
       ┌─────────────────┼────────────────┐
       ▼                 ▼                ▼
   Primary DB       Vector DB        Object storage
       │                 │                │
       ▼                 ▼                ▼
   Backups        Training corpus    LLM provider
   (next rotation) (exclude flag)    (zero-retention API)
                         │
                         ▼
                 [Erasure Certificate]
                 → emailed to user, stored 6 yrs
Two non-obvious points. Trained models don’t “forget” easily — true deletion requires retraining without that data. The Garante is currently lenient if you opted the user out of training and can prove the next cycle excludes them; don’t assume that holds past 2027. And use zero-retention API keys — otherwise your subprocessor is retaining data after you “deleted” it, which is a clean Article 17 violation laid at your feet.
International Transfers and Age Verification — The Two Cheap Wins
Almost every AI companion uses an LLM hosted in the US — a third-country transfer under Schrems II, requiring a Data Privacy Framework signup or SCCs, plus a Transfer Impact Assessment.
| Provider | Mechanism | EU residency | Zero-retention |
|---|---|---|---|
| OpenAI Enterprise | DPF + SCCs | Yes (Enterprise tier) | Yes — default on API |
| Anthropic Enterprise | DPF + SCCs | Yes (Enterprise) | Yes — default on API |
| Google Vertex AI | DPF + SCCs | Multiple EU regions | Configurable |
| Mistral (EU-native) | Not required | EU-native | Yes |
| Self-hosted on AWS Frankfurt | Not required if EU only | Full control | N/A |
The cheapest compliance path is the boring one: host inference in the EU. Hybrid setup (EU for EU users, US for the rest) is now table stakes. It also makes the country-of-registration decision easier — see our jurisdiction guide for NSFW AI companies.
On age verification: every major AI companion enforcement action since 2023 cited weak or absent age checks. A self-declared birthday is not age verification. What works: document-based (Veriff, Onfido, Sumsub, Yoti), credit-card-based 18+ checks (standard for adult payment processors), facial age estimation, or hard geofencing. Cost: €0.40–€1.50 per verified user. The fine for skipping it starts at €5 million.
GDPR + EU AI Act: The Dual Stack After August 2026
From 2 August 2026, you live under the AI Act’s main operational regime on top of GDPR. The two stack — one bad data flow can trigger fines under both.
| Provision | In force | What it means |
|---|---|---|
| Art. 5(1)(a) — manipulative AI | Feb 2025 | No techniques that materially distort behaviour. Engagement-maximising “always-agree” companions sail close to the wind. |
| Art. 5(1)(f) — emotion recognition | Feb 2025 | Banned in workplace/education. Consumer companions face heavy scrutiny. |
| GPAI model obligations | Aug 2025 | Fine-tune your own model → you inherit transparency + copyright + safety docs |
| High-risk system rules | Aug 2026 | Emotion-based recommendations or biometric ID can flip you into high-risk |
| Transparency to users (Art. 50) | Aug 2026 | Must tell users they’re interacting with AI; label AI-generated content |
| Penalties | Aug 2026 | Up to €35M / 7% turnover for prohibited; €15M / 3% for high-risk |
Even if you only ship a consumer app and never train your own model, the AI Act adds disclosure obligations on top of GDPR. Non-negotiable from August 2026.
The Compliance-First Architecture
Reference stack we deploy on every build:
┌────────────────────────────────────────────────┐
│            MOBILE / WEB CLIENT                 │
│  Granular consent UI · AI Notice banner        │
│  Erasure / portability self-serve              │
└──────────────────┬─────────────────────────────┘
                   ▼  TLS 1.3
┌────────────────────────────────────────────────┐
│   API GATEWAY (EU region — Frankfurt)          │
│   Geo-router → PII tokeniser → audit log       │
└──────────────────┬─────────────────────────────┘
                   ▼
┌────────────────────────────────────────────────┐
│   LLM PROVIDER (Zero-retention, EU endpoint)   │
│   Mistral / Anthropic EU / OpenAI EU           │
└──────────────────┬─────────────────────────────┘
                   ▼
┌────────────────────────────────────────────────┐
│   VECTOR DB + PRIMARY DB (EU region)           │
│   Per-user namespace · customer-managed keys   │
└────────────────────────────────────────────────┘
Full case studies of this pattern in production: Candy.ai and SugarLab.ai. Privacy architecture is identical — only the personality changes.
What It Actually Costs
Mid-2026 European market rates:
| Item | One-time | Annual |
|---|---|---|
| DPIA (lawyer + tech architect) | €8K–€25K | €3K refresh |
| Privacy notice + ToS + consent flow | €3K–€7K | €1.5K review |
| EU Representative (Art. 27) | — | €1.2K–€3.6K |
| DPO (fractional) | — | €18K–€60K |
| Age verification (per new user) | — | €0.40–€1.50 |
| Zero-retention LLM tier uplift | — | +15–40% over base API |
| EU inference infrastructure | — | ~+10% vs US |
| Pen test + Art. 32 review | €6K–€15K | €5K retest |
| Realistic first-year compliance budget | €20K–€55K | €30K–€80K |
Versus fines of €5M to €15M — compliance runs roughly 0.2-1% of your downside risk. Our mobile app cost calculator bundles privacy engineering into the estimate by default.
The 30-Day GDPR-Ready Build Checklist
If you read one section, read this.
Week 1 — Foundation
- Lawful basis for each processing activity, in writing (Art. 6)
- Data flow map on one page (in → process → store → share → delete)
- EU region for inference + storage; zero-retention LLM tier
- Appoint DPO (or fractional) and EU Representative (Art. 27)
Week 2 — Policies
- Privacy notice naming every category of personal and special category data
- ToS distinguishing contract basis from consent
- Granular consent UI (training opt-in OFF by default)
- Signed DPAs with every subprocessor
- Records of Processing Activities (Art. 30)
Week 3 — Build it in
- Document-based age verification at signup
- Erasure pipeline (fan-out per diagram above)
- Data portability export (Art. 20)
- Breach detection + 72-hour notification
- Audit logs on every Art. 9 read/write
- AI Notice banner (AI Act Art. 50)
Week 4 — DPIA, test, launch
- DPIA complete with legal + tech sign-off
- Privacy-focused penetration test
- Tabletop incident response drill
- Support team trained on subject access requests (30-day SLA)
- Then open EU signups
If you can’t tick those boxes, geofence the EU until you can. A fine costs more than four weeks of waiting.
Verdict
Compliance is now a product feature. Candy.ai, SugarLab.ai, the better-run DreamGF clones — their privacy UX is visibly tighter than competitors’. Users notice. App stores notice. Regulators definitely notice.
Doing it after launch is 5–10× more expensive than doing it before. Retrofitting consent into a live product means migrating records, re-collecting consent, and explaining the change without tanking conversion.
The fine ceiling rises on 2 August 2026. Planning a Q3 launch? Your DPIA needs to be done in Q2. That’s now.
Closing CTA
Two ways forward.
Pre-launch or under 10K users: Free 30-minute review with our NSFW chatbot development team — we review your data flows, flag the GDPR red lines, give you a written punch list. No sales theatre.
Over 10K users in the EU: You need a DPIA, defensible consent architecture, and a working erasure pipeline, in that order. Reach out via tripleminds.co/contact-us — mention “GDPR audit,” one business day turnaround.
White-label Candy.ai and DreamGF builds with the privacy stack baked in: Candy AI clone and DreamGF clone.
FAQs
Does GDPR apply to my AI companion startup if I’m based in the US?
Yes, if you offer the service to EU users or monitor their behaviour. Article 3(2) is extra-territorial. You must also appoint an EU Representative under Article 27 — the lack of one was a contributing factor in several recent enforcement actions.
When does the EU AI Act start applying on top of GDPR for AI companion apps?
The prohibitions and AI literacy duties applied from 2 February 2025. GPAI model obligations applied from 2 August 2025. Most remaining provisions — including transparency to users (Art. 50), high-risk system rules, and full penalty regime — apply from 2 August 2026. From that date a single bad data flow can trigger fines under both GDPR and the AI Act, stacked.
Do I have to do a DPIA before launching?
For an AI companion processing special category data at scale, yes — Article 35 makes it mandatory. From 2 August 2026, the maximum fine for missing one climbs to roughly €55 million under the stacked GDPR + AI Act regime.
Can I use OpenAI or Anthropic and still be GDPR-compliant?
Yes, but only on their enterprise / zero-retention tiers, with a signed Data Processing Agreement, EU data residency where offered, and a Transfer Impact Assessment on file. Consumer tiers are not suitable for processing EU user conversations.
How do I delete a user’s data from my AI model?
You can’t fully — not from a trained model. The compliance path: delete from all live systems, backups, caches and observability; flag the user as excluded from future training runs; issue an erasure certificate. Use zero-retention API tiers so your LLM provider isn’t holding logs you can’t reach.
Is a self-declared “I am 18+” checkbox enough for age verification?
No. Every major AI companion enforcement action since 2023 has cited it as inadequate. For 18+ content you need document-based, biometric, or credit-card-based age assurance.
Build the privacy stack like the regulator is your first user. Because eventually, they will be.
Disclaimer: We are the developers behind SugarLab.ai and have worked with industry leaders like Candy.ai and several other multi-million dollar NSFW businesses. We’ve successfully handled payment processor integration and orchestration for them—so we consider ourselves fully qualified to educate and guide you on NSFW Adult Payment Processors & Orchestration. That’s why we’re writing this blog.
Learn how to get approved by NSFW payment gateways for adult apps, chatbots, and high-risk platforms. Avoid bans with this [year] payment orchestration guide.
The global NSFW and adult content industry is booming—with new digital experiences like adult chatbots, AI companions, live cam platforms, and premium content apps leading the charge. Yet despite massive demand and user engagement, most entrepreneurs face a brutal reality early on:
- Their payment gateway gets rejected or suspended.
- Stripe, PayPal, Razorpay, and other mainstream providers don’t support NSFW content.
- Even when you get approved, your gateway may get banned after just a few transactions.
This blog is your complete guide to navigating the NSFW payment processor landscape—from finding compliant gateways to getting approved, staying compliant, and setting up a sustainable orchestration model for long-term growth.
Triple Minds: Experts in NSFW Payment Gateway Solutions & Adult App Development
At Triple Minds, we don’t just build NSFW platforms—we provide end to end solution like NSFW Chatbot Development, AI Development, AI Model Training, NSFW Payment Orchestration and Adult SEO Services. We are doing this for years. We marketed for Candy.AI, we developed sugarlab.ai and list is so on.
With years of experience in high-risk app development, payment gateway integration, and NSFW-specific compliance, we’ve helped dozens of adult startups:
- Get approved on NSFW-friendly payment processors like CCBill, Segpay, and Paxum.
- Develop and launch AI-based adult chatbots, subscription platforms, and cam apps.
- Sustain operations without the fear of sudden bans or chargeback-related shutdowns.
We know the adult space—technically, legally, and financially. This guide shares everything we’ve learned to help you avoid costly mistakes and build a profitable, policy-compliant NSFW product from Day 1.
Why You Need a Specialized NSFW Payment Processor
If you’re launching an adult app, NSFW chatbot, or high-risk platform, your first goal is clear: monetize safely and sustainably.
But here’s what most founders quickly discover—payment processing is the biggest obstacle in the adult space.
At Triple Minds, we’ve worked with dozens of adult platforms that got everything right—except their payment setup. The result?
- Accounts suspended weeks after launch
- Funds frozen for up to 6 months
- Apps taken offline with zero recourse
Here’s why this happens…
Mastercard & Visa: No Place for NSFW
Both Mastercard and Visa have very strict regulations around adult content. Their global network policies prohibit use of their systems for platforms involving:
- NSFW or sexually explicit content
- High-risk behavior
- User-generated adult material (even if moderated)
This means ANY payment gateway operating on Mastercard/Visa rails (like Stripe, Razorpay, PayPal, etc.) is bound by those rules—even if they don’t say it upfront.
You might get approved by Stripe or PayPal initially…
…but one flag, one complaint, or one algorithmic audit—and your account is gone.
Real-World Case Study: Candy.ai & Sweetdream.ai
Take Candy.ai, a leader in the NSFW AI chatbot industry. They knew better than to trust Stripe or PayPal—and instead use Wasabigate and PayMerchant, two adult-friendly processors built for high-risk transactions.
That’s what industry leaders do.
Now take Sweetdream.ai—a newcomer in the NSFW chatbot and AI image generation space.
Surprisingly, they’re still processing payments through Stripe.com—a mainstream gateway that, under Mastercard and Visa rules, clearly prohibits adult content. In fact, these card networks have rejected even some of the biggest industry players.
And yet, Stripe approved Sweetdream?
The reason is simple: they’ve worked with a smart payment orchestration company like Triple Minds that knows exactly how to position and present platforms to pass approval, even in grey zones.
Want names? Trust us, we have them. We’ve been on calls with top platforms banned by Mastercard.
Still think this is luck? It’s not.
If you’re serious about getting paid and staying approved in the NSFW space, schedule a call with our NSFW Payment Orchestration Expert today.
We’ll show you:
- Who’s really processing what
- How to get approved
- And how to build a resilient system that won’t collapse after one compliance review
Here’s What Triple Minds Knows (That Most Don’t)
The adult tech industry is full of grey zones, loopholes, and moving goalposts.
But we’ve been on the inside.
We know:
- Which NSFW payment processors actually approve adult AI, cam, or content platforms
- What terms and content triggers lead to rejection (AI-generated, synthetic, real, animated—each has its own rulebook)
- The “quick fixes” and compliance tricks that can save a platform before it gets banned
- How to build hybrid payment orchestration systems using crypto, adult processors, and smart routing logic
If you’re new to this space, chances are you’ll get rejected—even if your platform is legit.
That’s where Triple Minds steps in.
We don’t just integrate your gateway—we prepare your business for approval, handle compliance, and create fallback systems so your cash flow never stops.
The Sure-Shot Solution for NSFW Payment Processing: Orchestrate It
If you’re serious about getting a NSFW payment processor approved without getting suspended later, here’s the sure-shot solution: You need to follow the Payment Orchestration method.
This isn’t just a recommendation—it’s the standard used by all leading adult platforms today. From global cam sites to top AI chatbots, payment orchestration is how they securely manage compliance, approvals, and multiple payment gateways without risking shutdowns.
Don’t worry—we’ll guide you step by step in this article.
You’ll learn:
- What payment orchestration actually means
- Why it’s crucial for NSFW & high-risk platforms
- And most importantly, how to implement it in your adult project with help from Triple Minds.
This isn’t guesswork. These are field-tested guidelines we use to build safe, scalable, and fully approved adult platforms.
How Payment Orchestration Works
A step-by-step flowchart from the customer’s click on the payment page to the final confirmation.
Payment Page
The customer enters their card or other payment details and clicks “Pay Now”.
Payment Orchestrator
Secure payment data is sent to the Payment Orchestration Platform instead of a single gateway.
Dynamic Routing
Rules (lowest cost, highest success rate, currency, risk score) pick the best gateway for this transaction.
Payment Gateways
Bank Authorization
The selected gateway sends the transaction to the acquirer and card network for authorization.
Bank Response
Bank returns “Approved” or “Declined”.
Response to Orchestrator
Gateway forwards the bank’s response back to the orchestrator.
Update System
Orchestrator updates your systems (CRM, ERP, analytics, fulfillment) with the result.
Retry Logic (Optional)
On failure, the orchestrator can automatically retry via a different gateway to save the sale.
Thank You Page
Customer is redirected to the confirmation page with success or failure status.
What is NSFW Payment Processing & Payment Orchestration?
Let’s break this down like we do on our consultation calls—no jargon, just real talk.
NSFW Payment Processing – What Does It Actually Mean?
NSFW payment processing simply means: How you collect money (credit card, wallet, crypto, etc.) on a platform that offers adult or “Not Safe For Work” content.
The challenge? You can’t just slap Stripe or Razorpay onto an adult app and start charging users. These processors follow Mastercard and Visa rules, which clearly say:
❌ No adult content
❌ No sexual chatbots
❌ No high-risk subscription models
So, you need payment gateways that are okay with adult content—these are called NSFW-friendly processors (like CCBill, Segpay, Paxum, etc.).
But here’s the twist…
Even with these adult processors, getting approved isn’t automatic. You still need proper documentation, compliance setup, risk handling, and a solid reputation.
And that’s where Payment Orchestration comes in.
What is NSFW Payment Orchestration?
Payment Orchestration is how you manage multiple payment processors smartly, so your platform doesn’t rely on one risky provider.
Imagine you own a restaurant. Would you rely on just one food supplier to deliver everything every day?
Probably not—because if they fail, your business stops.
Payment orchestration works the same way. It means creating a smart payment setup where:
- You don’t depend on one payment gateway
- You can switch between multiple processors if one goes down or gets blocked
- You can route different transaction types through different gateways (e.g., subscriptions via CCBill, tips via crypto, payouts via Paxum)
It’s like having a backup plan, fallback system, and smart switchboard—all rolled into one.
Real Example from Our Clients
We recently helped a client building an AI-based NSFW chatbot. They initially integrated Stripe (which approved them).
Two weeks later—account suspended, funds frozen. No warning.
Why? Stripe’s backend flagged the term “virtual girlfriend” in one of the chatbot scripts.
We stepped in, set up:
- Segpay for subscription billing
- Paxum for creator payouts
- Crypto wallet via NowPayments for anonymous users
Now, even if one processor fails, the business keeps running.
That’s payment orchestration—and it’s the only reason this client didn’t go bankrupt.
At Triple Minds, we help NSFW founders not only get the right processors—but we build you a resilient orchestration layer so your revenue never stops, and you don’t have to wake up worried about account bans.
Top NSFW Payment Gateways in 2025 & How to Choose the Right One
Not all NSFW platforms are the same—some sell subscriptions, others offer tipping, pay-per-minute chats, image generation, or custom AI bots. That means choosing the right NSFW payment processor isn’t about picking the most popular one—it’s about picking the right one for your business model.
At Triple Minds, we don’t just integrate processors—we analyze your product, pricing model, region, and risk level to recommend a solution that’s fast to approve, safe long-term, and optimized for global growth.
The best NSFW-friendly payment processors trusted by adult platforms in 2025 are: CCBill, Segpay, Verotel, Epoch, Paxum, and crypto gateways like NowPayments. These processors are built to handle adult content, recurring billing, global compliance, and creator payouts—making them the backbone of high-risk payment orchestration.
How to Get Approved on a NSFW Payment Gateway (Without Getting Banned)
Getting approved on a NSFW-friendly payment processor isn’t just about applying and waiting.
It’s about how you present your platform, what documents you submit, and whether your system meets compliance from day one.
At Triple Minds, we’ve helped NSFW platforms pass approvals that others failed—because we follow a proven orchestration method that processors trust.
Here’s the Step-by-Step Approval Process:
1. Choose the Right Gateway Based on Your Business Model
Subscription? Tipping? Creator payouts? We match your use case with the right processor.
2. Prepare Your Compliance Documents
You’ll need:
- Terms of Service & Privacy Policy (must mention age restrictions)
- Proof of 18+ content moderation
- KYC details for your business & domain
- Secure checkout with SSL
3. Structure Your Platform for Approval
We help configure:
- Proper user flows (e.g., no free NSFW access before age verification)
- Clear refund & chargeback policies
- Clean UI that reflects legitimacy and safety
4. Submit the Application (With the Right Framing)
What you say in your application matters. We help you position your platform smartly so it doesn’t get flagged under Visa/Mastercard rules.
5. Setup Multiple Gateways (Orchestrated)
Even after approval, your job isn’t done.
We set up orchestrated backups—so if one gateway pauses or reviews your account, others continue processing smoothly.
Why Most NSFW Startups Get Rejected
- Vague or missing policies
- Using Stripe or PayPal without disclosure
- Poorly framed product descriptions
- User-generated content without moderation
- No age-gating, or adult content visible before login
Triple Minds’ Payment Orchestration = Approval + Stability
We don’t just help you “get approved”—we help you stay approved.
Our orchestration model ensures:
- Faster approvals
- Lower risk of suspension
- Multiple processors in rotation
- Peace of mind while scaling
Want guaranteed compliance + multiple revenue routes?
We’re the team NSFW startups call before their gateway bans them.
Ready to build a compliant, profitable NSFW platform?
Common Mistakes That Get NSFW Platforms Banned After Approval (And How to Avoid Them)
Getting approved on a NSFW payment processor is a win.
But staying approved? That’s the real challenge.
We’ve seen platforms pass gateway checks and start earning—only to get banned after a few days or weeks because of simple, avoidable errors.
Here’s what you need to watch out for:
1. Using Banned Keywords in Product or Chatbot Descriptions
Even approved platforms can trigger Mastercard/processor flags by showing terms like “underage,” “teen,” “incest,” or even “virtual girlfriend” if phrased wrong. We audit your entire content structure before submission.
2. Exposing NSFW Content Before Age Verification
If your homepage, previews, or chatbot show anything adult without a verified login, you’re breaking compliance instantly. Triple Minds designs gated flows that are approval-friendly.
3. Accepting Payments via Stripe or Razorpay in Parallel
Trying to “sneak in” payments through a non-compliant gateway (while running an NSFW platform) is a red flag. We replace them with legal, adult-friendly processors through smart orchestration.
4. Not Moderating User-Generated Content (UGC)
If your app allows uploads or AI-generated images, you must track, moderate, and document everything. We set up UGC policies + moderation dashboards that are approval-proof.
5. Ignoring Local Compliance (Especially EU, U.S., and India)
Not all payment processors are allowed in every region, and your gateway could get blocked due to local financial laws. We customize payment flows based on your operating country.
Triple Minds Helps You Build Ban-Proof Payment Architecture
At Triple Minds, we do more than just help you “pass checks”—
We help you avoid the mistakes that cause suspensions, blacklisting, or legal issues.
We:
- Review your entire product before submission
- Set up compliant content & flow
- Integrate multiple payment routes (credit card, crypto, wallet)
- Run ongoing audits to keep you safe as you scale
How Triple Minds Builds NSFW Payment Architecture That Doesn’t Break
At Triple Minds, we don’t just “integrate a payment gateway” — we build NSFW payment infrastructure that can withstand bans, audits, policy changes, and high-risk flags.
Whether you’re launching an AI chatbot, cam platform, or content marketplace — your monetization engine needs to be built like a vault: resilient, compliant, and ready for scale.
Here’s How We Build It, Step by Step:
1. Payment Stack Strategy Based on Business Model
We start by understanding what you’re selling — subscriptions, tokens, tips, or pay-per-download — and match it with the best gateway(s).
2. Multi-Gateway Setup (Payment Orchestration)
We don’t rely on one processor. Instead, we integrate:
- Primary gateway (like Segpay or CCBill)
- Backup processor (Verotel, Epoch, etc.)
- Crypto gateway (NowPayments, BitPay, etc.)
- Payout solution (Paxum or bank wire)
So if one fails, others auto-activate — and your business never stops.
3. Region-Specific Compliance Layer
India? EU? U.S.?
Every country has its own rules. We tailor payment flows and hosting setups per region, so you’re safe across borders.
4. Content & UX Compliance Filters
We restructure content and chatbot UI/UX to:
- Block NSFW previews before login
- Pass age-gating and 2257 checks
- Remove flagged keywords
5. Payout & Risk Management
We don’t just collect money — we help you distribute it legally and safely to creators, affiliates, or partners.
Real Clients, Real Results
One of our recent clients had their app banned 3 times before we stepped in.
We rebuilt their payment flow using a multi-gateway orchestration system, removed content triggers, and added crypto for fallback.
They’ve now processed over $500K+ in transactions — no flags, no bans.
Conclusion
In the NSFW industry, getting approved on a payment gateway isn’t enough—you need a system that won’t collapse overnight. At Triple Minds, we build complete payment orchestration architecture tailored for adult platforms—combining multiple gateways, regional compliance, secure payouts, and long-term stability. We don’t guess—we implement what works. If you’re building an NSFW app, chatbot, or content platform, let’s make your payments bulletproof and ban-proof.
Stripe and PayPal are prohibited from processing payments for adult content due to the strict network policies of Mastercard and Visa. Using them for an NSFW business will result in a sudden account ban and your funds being frozen.
The best payment processors for NSFW content are specialized high-risk gateways. Top-rated options for 2025 include CCBill, Segpay, Verotel, Epoch, and Paxum. For crypto transactions, NowPayments is a leading choice.
NSFW payment orchestration is the strategy of using multiple payment gateways at once. You need it to ensure business continuity; if your primary processor bans or blocks you, the system automatically reroutes payments to a backup gateway, preventing any loss of revenue.
Triple Minds builds a complete, ban-proof payment orchestration system for your NSFW business. We manage the entire process for you—from selecting the right gateways and preparing compliance documents to handling the application and setting up multiple backup processors to guarantee your revenue is secure.